Holistic AI EndLayer Guardian Agents for AI.
See and control every AI tool your company uses. EndLayer finds the AI on every laptop, shows you the risk and blocks unsafe prompts and secrets before they leave the machine.
one agent · one laptop reporting in a minute
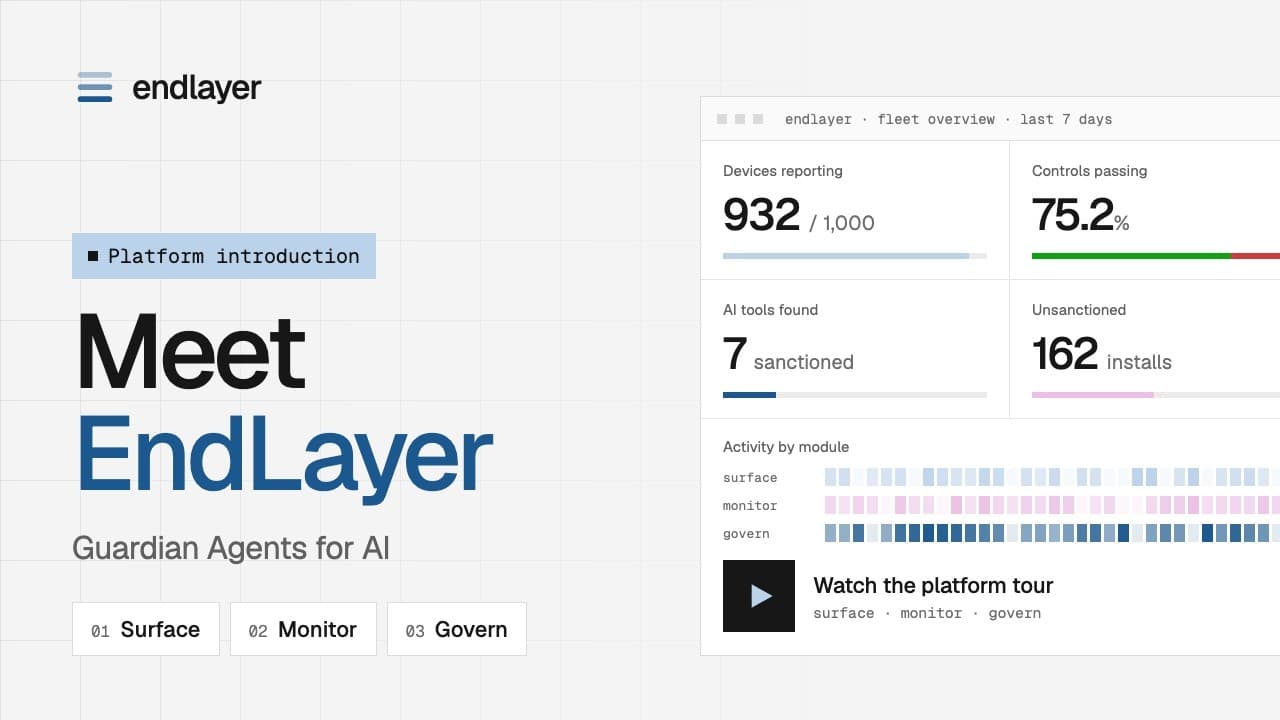
See EndLayer at work.
A two minute introduction to EndLayer: how the Layer 1 Agent finds every AI tool, agent, model and key on a laptop, shows what they reach and cost, and enforces your AI policy on the device as it happens.
Read the transcript
0:00 The problem. Every day, someone in your company tries a new AI tool. A coding agent to finish the sprint, a chatbot to write the report, a local model just to see what it can do. Nobody means any harm, but nobody told security either. Now multiply that by every laptop you own. Agents that act on their own, keys left in files, company data on personal accounts. None of it crosses your gateway. So when the board asks, “What AI are we running?”, the honest answer is, “We don’t know.” That changes now.
0:39 Meet EndLayer. Meet EndLayer, Guardian Agents for AI. One agent on every device, the Layer 1 Agent, and one place to see and govern all of your AI.
0:51 Surface. First, it surfaces everything. Every AI tool, agent and model, every MCP server, every key sitting in a file. A tool installed at 9:00 is in your inventory by quarter past.
1:06 Monitor. Then it shows you what matters. Which agents can act without a human, which accounts are personal, and what it all costs, team by team.
1:15 Govern. And then you decide. Write your policy once, and every device is checked against it. When someone pastes a card number into an AI tool, the Layer 1 Agent stops it before it ever leaves the machine. Every decision is kept. So when the auditor asks, you don’t scramble. You show them.
1:38 One agent. All of this runs on one agent, the Layer 1 Agent. It finds what a network never will. It reads AI traffic on the machine that made it, and it stops what your policy forbids as it happens. There is no language model on the device, and only redacted evidence ever leaves. Your people keep working, and security can finally see.
2:02 Close. AI is already inside your company. Now you can see it, govern it, improve it. EndLayer by Holistic AI. Book your demo at endlayer.ai.
AI adoption is outpacing your security controls.
Employees adopt AI apps, coding agents and MCP servers faster than IT can review them. Most of it runs on the endpoint, out of reach of your CASB, proxy and SSO.
No inventory of AI in use
Desktop apps, coding agents, local models and browser AI never pass through your gateway, so they never reach your asset register.
Sensitive data leaving through AI
Source code, customer records and API keys flow into personal ChatGPT and Claude accounts, with no audit trail behind them.
Policies that exist only on paper
Your AI acceptable use policy has no enforcement point on the device, and no evidence to show the board or an auditor.
Discover, monitor and govern every AI tool from one console.
A lightweight agent on each endpoint feeds three modules. It deploys through Intune, Jamf or your existing tooling, with no proxy and no network change.
Complete visibility into shadow AI
A live inventory of every AI app, coding agent, MCP server and model across your fleet, sanctioned or not.
- Automatic discovery on every endpoint, with no integration to build
- MCP servers mapped with the credentials they hold
- AI website usage in the browser
Continuous AI risk monitoring
Every finding is tied to a user, a device and a cost, so your team can act on what matters first.
- Personal accounts used for corporate work
- Exposed API keys and secrets on disk
- Autonomous agents running unattended
- Token spend attributed by team and project
Policy enforcement at the endpoint
Publish your AI policy once. EndLayer enforces it on every device and keeps a versioned record of every decision.
- Guardrails that block secrets and sensitive data in real time
- Findings routed to an owner and tracked to closure
- Audit evidence mapped to SOC 2, the EU AI Act and ISO/IEC 42001
A prompt to ChatGPT held an AWS key. It was stopped on the device, and the key never left the laptop.
One agent on the device. Nothing on your network.
Including whether a coding agent may act unattended. All 21 →
A tool installed at 9:00 is in the inventory by 9:15.
Mac, Windows, Linux, iOS, Android, servers and cloud.
It runs as the user and never elevates.
Three ways in.
Log in and use it now.
Sign up, install the agent, and the first device reports in a minute.
Or run it on your own servers.
Nothing about your devices leaves your network.
A small free tool.
What AI ran on one machine, and what it cost. Not the platform.
Partners are already selling EndLayer. Here is the pipeline.
- partners in the programme
- 11
- partners in the pipeline
- 50
- open opportunities
- 150
- devices across those accounts
- 150,000
As of October 2026. 3 opportunities per pipeline partner on average, each an account of 1,000 or more devices.
The seven we are asked first.
What is EndLayer?
EndLayer is Guardian Agents for AI. One agent, the Layer 1 Agent, runs on every device with no admin rights and no proxy or gateway. It finds shadow AI (every tool, coding agent, model, MCP server, account and API key in use), shows the risk each one carries and what it costs, and checks all of it against the policy you publish. Guardrails in the agent warn, redact or block as it happens. Surface, Monitor and Govern are the three modules, and EndLayer is a product of Holistic AI.
Does it read our conversations?
Yes, for PII leaking into a prompt, and for tools being used in ways nobody authorised. It is not on by default, and turning it on records who enabled it and the reason why. Your admin can narrow what is collected at any time, and the agent cannot widen it.
Do we have to put a proxy or gateway in the path?
No. Nothing changes on your network. Everything is read from files already on the disk, which is also why desktop apps, coding agents and local models show up at all. none of them go through a gateway.
Does the agent need admin rights?
No. It runs as the person using the machine and reads only what that account can already read. It never elevates, and it never executes any of the AI tools it finds.
What if we use a tool that is not on your list?
Seventeen are recognised by name. Anything else still surfaces as an unidentified AI process with the account and the machine attached, and naming it properly takes a signature, not an integration, so there is no work per tool for you either way.
How quickly does something new appear?
Within fifteen minutes. Every device sends a snapshot every fifteen minutes, so a tool installed at 9:00 is in the inventory by 9:15.
Can it block anything, or does it only watch?
Both. Every signal is measured against your policy version, and what fails gets an owner, a state and a date it closed. Guardrails inside the agent act on the device in real time: prompts are scored before they run, and secrets and personal data are warned on, redacted or blocked on the way out. Removing an installed app is the one action that waits for a person: an administrator approves the request before anything is uninstalled. Every action is recorded.
Take control of the AI already in your company.
It is already installed on the laptops. You can see all of it by this afternoon.